What Is Networking in Cyber Security?
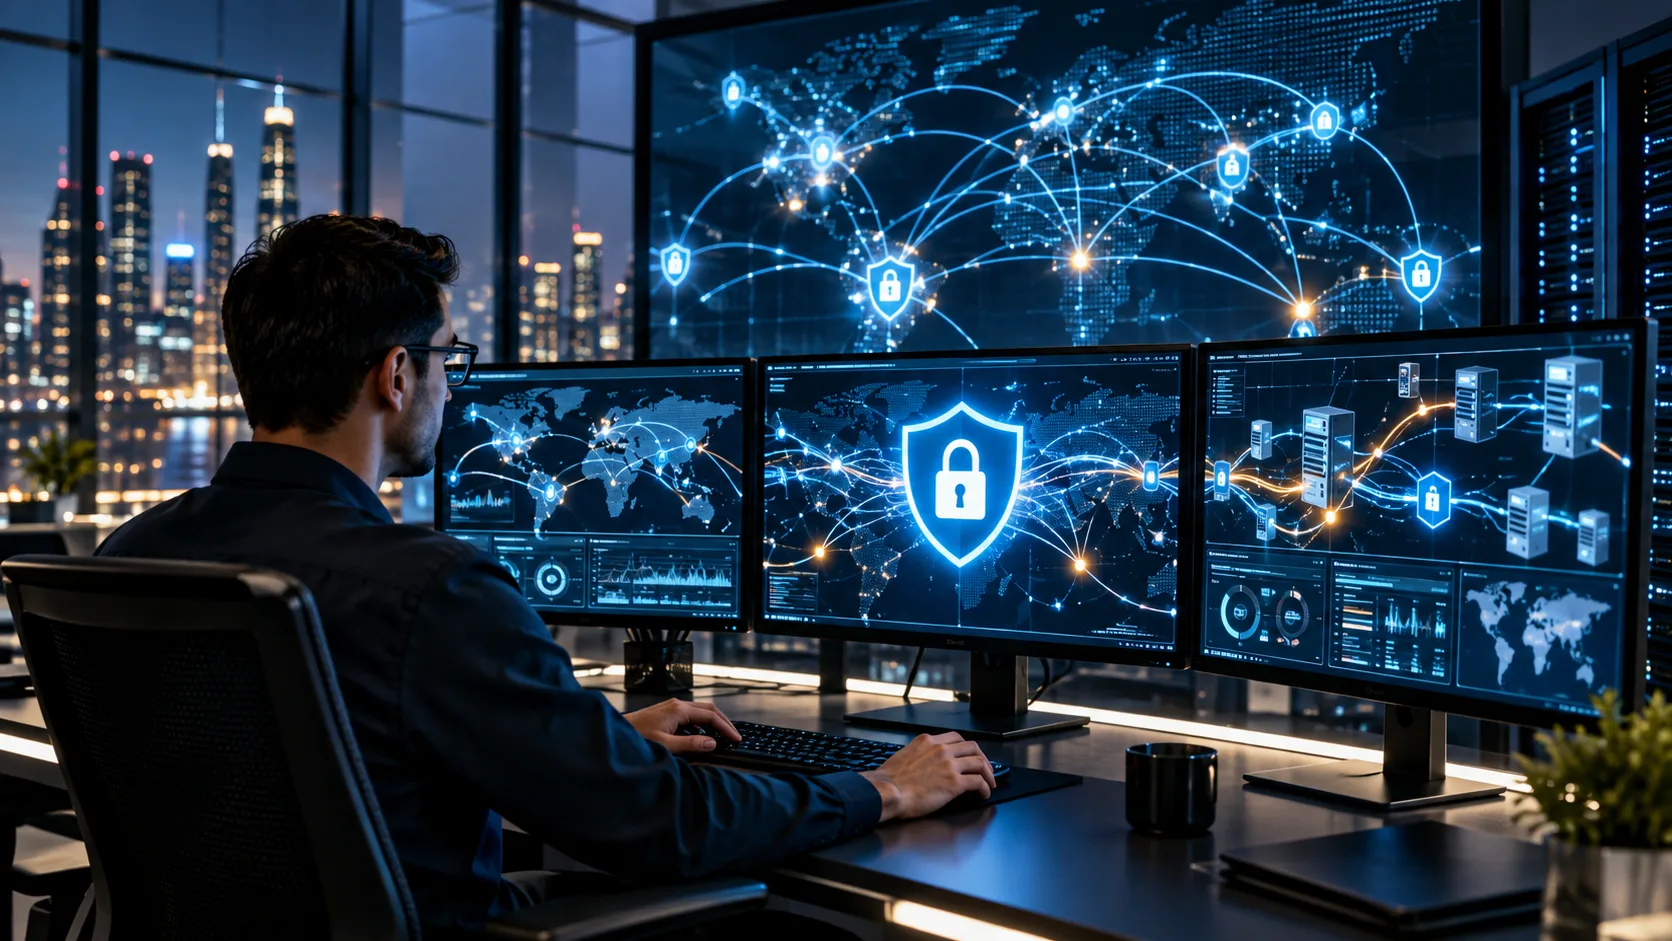
Networking in cyber security refers to the practice of protecting computer networks, connected devices, systems, and data from unauthorized access, cyberattacks, misuse, and disruption. It combines traditional networking principles with security technologies to ensure information can move safely between users, servers, applications, and devices without being intercepted, modified, or stolen by attackers.
Modern organizations depend heavily on networks to connect employees, cloud platforms, websites, databases, applications, and business systems. Every connection creates a potential entry point for cybercriminals, which makes network protection an essential part of an overall cybersecurity strategy. Effective network security focuses on confidentiality, integrity, availability, authentication, access control, and continuous monitoring.
Understanding networking is also important for anyone interested in cybersecurity because many attacks happen through network infrastructure. Security professionals must know how devices communicate, how IP addresses work, how traffic travels, and where vulnerabilities can appear. Learning [network security basics](Add link here) can provide a useful foundation for understanding how organizations protect connected systems against common digital threats.
How Networking and Cyber Security Work Together
Networking allows computers, servers, phones, cloud services, and other devices to communicate through wired or wireless connections. Cyber security adds protective controls around those connections so sensitive information does not become exposed while moving across a network. Without security protections, attackers may intercept communications, access systems, steal credentials, or disrupt normal business operations.
Cybersecurity teams analyze network traffic to understand what devices are communicating and whether those communications are legitimate. Security technologies can identify suspicious login attempts, unusual traffic patterns, malware activity, unauthorized connections, and unexpected data transfers. This visibility allows organizations to detect potential threats before attackers cause serious damage to systems or sensitive information.
Networking knowledge also helps security professionals understand where attacks may originate and how they spread. For example, an attacker who compromises one poorly protected device may attempt to move through the network and access other systems. Network segmentation, access restrictions, authentication, and monitoring can limit this movement and reduce the potential impact of a security incident.
Why Networking Is Important in Cyber Security
Most digital services depend on networks, making network infrastructure one of the most common targets for cybercriminals. Websites, email platforms, cloud applications, employee devices, databases, and internal business tools communicate through interconnected systems. If attackers gain unauthorized access to the network, they may be able to reach valuable information or disrupt critical services.
Secure networking helps organizations protect confidential customer information, financial records, intellectual property, employee data, and internal communications. Businesses can establish security policies that determine who can access specific systems and what actions they can perform. Strong controls also reduce the possibility that unauthorized users will gain access simply because they are connected to the organization’s network.
Network security is equally important for maintaining business continuity. Attacks such as ransomware, distributed denial-of-service incidents, and malware infections can interrupt operations and prevent employees or customers from accessing essential services. Proper network design, monitoring, backup strategies, and incident response procedures help organizations reduce downtime while recovering more quickly from security events.
Key Components of Network Security
Firewalls are among the most common components used to secure networks. A firewall examines incoming and outgoing network traffic and applies predefined security rules to decide whether connections should be allowed or blocked. Modern firewalls may also include application awareness, malware detection, intrusion prevention, content filtering, and advanced threat protection capabilities.
Intrusion detection systems and intrusion prevention systems provide another important layer of protection. These technologies analyze network traffic for suspicious behavior or known attack patterns. An intrusion detection system typically generates alerts when unusual activity appears, while an intrusion prevention system may automatically block or restrict potentially malicious traffic before it reaches protected systems.
Other common network security components include virtual private networks, secure routers, authentication systems, endpoint protection, encryption, access control lists, and security monitoring platforms. Organizations often combine multiple technologies rather than relying on a single defensive solution. This layered security approach makes it more difficult for attackers to bypass protections and compromise critical resources.
Understanding Network Traffic in Cyber Security
Network traffic describes the data moving between devices, systems, applications, and online services. Security professionals examine this traffic to determine whether communication is normal, suspicious, or potentially malicious. Every request, connection, file transfer, login attempt, and application interaction can provide information about what is happening across a network environment.
Traffic analysis may reveal indicators of cyberattacks before users notice any obvious problems. For example, an infected computer might suddenly communicate with an unfamiliar external server or transfer unusually large amounts of data. Security monitoring systems can identify these patterns and alert administrators so they can investigate suspicious activity before the incident becomes more serious.
Organizations may also establish a baseline of normal network activity. This baseline helps security teams recognize unusual behavior, such as connections occurring at unexpected times, devices communicating with unfamiliar destinations, or employees accessing resources they normally never use. Behavioral monitoring can be especially helpful for detecting sophisticated threats that traditional signature-based security tools might overlook.
Common Network Security Threats
Malware is one of the most common threats affecting computer networks. Viruses, ransomware, worms, spyware, and trojans can enter through malicious downloads, infected email attachments, compromised websites, or vulnerable devices. Once inside, certain types of malware can spread between connected systems, steal sensitive information, damage files, or provide attackers with ongoing remote access.
Phishing and credential theft can also lead to network security incidents. Attackers frequently trick employees into revealing passwords or signing into fake websites. Once credentials have been stolen, cybercriminals may attempt to access internal services, cloud platforms, email systems, or remote network connections while appearing to be legitimate users.
Other threats include man-in-the-middle attacks, denial-of-service attacks, spoofing, unauthorized access, DNS attacks, malicious insiders, and exploitation of unpatched vulnerabilities. The specific risks depend on an organization’s infrastructure and operations. Regular vulnerability assessments, software updates, access management, user training, and network monitoring can help reduce exposure to these threats.
What Is a Firewall in Network Security?
A firewall acts as a security barrier between trusted networks and potentially dangerous connections. It monitors network traffic according to configured rules and decides whether particular connections should be permitted. Firewalls can be deployed as physical appliances, software applications, cloud-based services, or integrated components within routers and other network infrastructure.
Traditional firewalls often make decisions based on information such as IP addresses, ports, and protocols. More advanced next-generation firewalls can inspect applications, users, encrypted traffic, and specific content. These additional capabilities help organizations identify suspicious activity that might otherwise appear to be legitimate network communication.
Firewall rules must be configured carefully because overly permissive policies may expose systems unnecessarily. Organizations should allow only the connections and services required for legitimate business activities. Regularly reviewing firewall configurations also helps remove outdated rules, identify unnecessary access, and ensure security controls continue to reflect the organization’s current infrastructure.
What Is Network Segmentation?
Network segmentation involves dividing a large network into smaller, separate sections. Instead of allowing every connected device to communicate freely with every other system, organizations establish boundaries between different groups of resources. These segments might separate employees, servers, payment systems, guest Wi-Fi, development environments, databases, and critical infrastructure.
Segmentation improves security because attackers who compromise one section of the network may have difficulty reaching other areas. For example, a compromised employee laptop should not automatically provide access to sensitive financial servers. Firewalls, virtual LANs, access control policies, and software-defined networking technologies can help enforce communication restrictions between network segments.
This approach can also make security monitoring easier. When organizations understand which systems should communicate with each other, unexpected connections become easier to identify. Segmentation supports the principle of least privilege by limiting users and devices to only the resources they genuinely require, reducing the potential attack surface available to cybercriminals.
Role of IP Addresses and Ports in Cyber Security
An IP address identifies a device or network interface so data can be routed to the correct destination. Cybersecurity professionals frequently analyze IP addresses when investigating suspicious connections, unauthorized login attempts, malware communications, or unusual network behavior. Both internal and external addresses can provide valuable context during security investigations.
Ports help identify specific services or applications running on a device. Common services use particular port numbers, although configurations may vary between environments. Attackers often scan systems for open ports because exposed services can reveal potential entry points, especially when those services are outdated, misconfigured, or protected by weak authentication.
Security teams regularly review open ports and disable unnecessary services to reduce risk. Firewalls can also restrict which addresses are allowed to communicate with specific ports. Combining port management with vulnerability scanning, software patching, authentication, and monitoring helps prevent attackers from exploiting unnecessary or poorly secured network services.
Wireless Network Security
Wireless networks provide convenient access but can introduce additional security challenges because communication travels through radio signals rather than physical cables. Attackers within range may attempt to intercept connections, guess passwords, impersonate legitimate wireless networks, or exploit outdated wireless security standards. Proper configuration is therefore essential for protecting Wi-Fi environments.
Organizations should use modern encryption standards, strong passwords, secure authentication methods, and properly configured wireless access points. Guest networks should usually remain separated from sensitive internal systems. Administrators should also change default credentials and regularly update access point firmware to reduce exposure to known security vulnerabilities.
Employees should be careful when connecting to public Wi-Fi networks because these networks may not provide strong security. Using secure HTTPS connections and trusted virtual private networks can reduce certain risks while working remotely. Organizations may also implement endpoint security and remote access policies to protect employees who frequently connect from external locations.
What Is a VPN in Cyber Security?
A virtual private network creates an encrypted connection between a device and another network or VPN server. Encryption makes transmitted information much harder for unauthorized individuals to read while it travels across untrusted networks. Businesses frequently use VPNs to provide employees with secure remote access to internal resources.
Corporate VPNs typically require authentication before users can connect. Once verified, employees may access approved systems as though they were connected directly to the organization’s internal network. Security teams can restrict VPN access according to job responsibilities, device security requirements, location, or other risk factors.
VPN technology provides useful protection, but it should not be treated as a complete cybersecurity solution. Compromised credentials, infected endpoints, weak authentication, or vulnerable VPN software can still create serious risks. Multi-factor authentication, software updates, endpoint protection, and access monitoring should therefore complement VPN deployments.
Network Security Monitoring and Threat Detection
Network monitoring gives cybersecurity teams continuous visibility into activity across infrastructure. Monitoring tools can collect logs, analyze traffic, track device behavior, and identify suspicious connections. Instead of waiting for users to report problems, organizations can use automated systems to detect unusual activity and generate alerts for security teams.
Security information and event management platforms often collect information from firewalls, servers, applications, authentication systems, and network devices. Analysts can compare data from multiple sources to understand whether suspicious events are connected. This centralized visibility is especially valuable when investigating incidents that affect several systems simultaneously.
Modern threat detection increasingly includes behavioral analytics, machine learning, and automated response capabilities. These technologies may identify subtle changes that indicate compromised accounts or infected devices. However, human analysts remain important because automated alerts require context, investigation, and judgment before organizations can determine whether genuine security incidents have occurred.
Access Control and Authentication in Network Security
Access control determines who can connect to network resources and what they are permitted to do after gaining access. Organizations should avoid giving every employee unrestricted access to all systems. Instead, permissions should reflect job responsibilities, business requirements, and the principle of least privilege.
Authentication verifies that users, devices, or applications are genuinely who they claim to be. Passwords remain widely used, but passwords alone may not provide sufficient protection for sensitive systems. Multi-factor authentication adds another verification step, such as a security key, authentication application, or biometric factor, making stolen credentials less useful to attackers.
Network access control technologies can also evaluate devices before permitting them onto protected networks. Organizations may check operating system versions, security software, device identity, or compliance status. Devices that fail security requirements can be blocked, restricted, or placed into isolated network segments until administrators resolve the identified problems.
How Encryption Protects Network Communications
Encryption converts readable information into encoded data that unauthorized users cannot easily understand. When information travels across networks, encryption reduces the risk that attackers can read sensitive content if they intercept the communication. Secure websites, email services, VPN connections, messaging applications, and cloud platforms commonly rely on encryption technologies.
Transport Layer Security is widely used to protect communications between web browsers and websites. When HTTPS appears in a web address, TLS typically encrypts the connection between the user and the website. Encryption helps protect login credentials, financial information, personal details, and other sensitive data while it moves across the internet.
Encryption must be combined with proper key management and secure configuration. Weak protocols, expired certificates, poor implementation, or stolen encryption keys may reduce protection. Security professionals regularly review cryptographic standards and configurations to ensure organizations continue using secure technologies as older encryption methods become vulnerable or obsolete.
Zero Trust and Modern Network Security
Traditional security models often assumed that users or devices inside a corporate network could be trusted more than external users. Modern organizations increasingly operate across cloud services, remote workplaces, mobile devices, and third-party platforms. These changes have made network location alone an unreliable way to determine whether access should be trusted.
Zero Trust security follows the principle of never automatically trusting a user or device simply because it is already connected to the network. Every access request should be verified based on factors such as identity, device condition, location, requested resource, and risk level. Permissions should also remain limited to what users genuinely need.
Zero Trust can involve technologies including identity management, multi-factor authentication, network segmentation, endpoint protection, conditional access, continuous monitoring, and least-privilege permissions. It is not a single product that organizations install. Instead, it represents a broader security strategy designed to continuously verify access throughout modern distributed environments.
Best Practices for Secure Networking
Organizations should begin by maintaining a clear inventory of connected devices, applications, servers, cloud platforms, and network infrastructure. Unknown systems are difficult to protect because security teams may not know they exist. Asset management helps administrators identify outdated devices, unnecessary services, unsupported software, and potential vulnerabilities requiring attention.
Regular software updates and security patches are equally important. Cybercriminals frequently exploit known vulnerabilities when organizations delay updates. Vulnerability scanning and penetration testing can identify weaknesses before attackers discover them, while strong password policies and multi-factor authentication reduce the risk of unauthorized access caused by compromised credentials.
Organizations should also combine technical defenses with employee awareness and documented security procedures. Firewalls, encryption, monitoring, segmentation, endpoint protection, backups, and incident response plans work best when they support one another. Regular security reviews help businesses adapt their defenses as infrastructure, employees, technologies, and cyber threats continue to change.
Careers That Combine Networking and Cyber Security
Many cybersecurity careers require a strong understanding of computer networking. Network security engineers design and maintain secure infrastructure, while security analysts monitor traffic and investigate suspicious activity. Penetration testers, incident responders, security architects, cloud security specialists, and security operations center analysts also regularly work with networking technologies.
Professionals entering these fields usually benefit from understanding TCP/IP, DNS, DHCP, routing, switching, firewalls, VPNs, network protocols, wireless technologies, and common security threats. Practical experience with network configuration and traffic analysis can make cybersecurity concepts easier to understand because learners see how communication actually occurs between systems.
Beginners can build skills using virtual labs, networking simulators, home labs, cloud environments, and cybersecurity training platforms. Learning networking before advanced security topics often provides valuable context for understanding attacks and defenses. A strong networking foundation helps professionals recognize suspicious behavior and design security controls that fit real-world infrastructure.
Conclusion
Networking in cyber security focuses on protecting the connections that allow computers, applications, servers, cloud platforms, and users to communicate. Because modern organizations depend heavily on interconnected systems, network security plays an essential role in preventing unauthorized access, information theft, malware infections, and service disruption.
Effective protection requires multiple security layers rather than a single tool. Firewalls, encryption, segmentation, VPNs, authentication, monitoring, endpoint security, access controls, and vulnerability management all contribute to stronger network defenses. These technologies become more effective when organizations regularly review configurations and respond quickly to emerging security risks.
For anyone beginning a cybersecurity career, networking is one of the most valuable areas to understand. Knowing how data travels, how devices communicate, and how attackers exploit network weaknesses makes advanced security concepts easier to learn. Strong networking knowledge creates a practical foundation for protecting systems in increasingly connected digital environments.
FAQs
What is networking in cyber security in simple words?
Networking in cyber security means protecting computers, devices, servers, and data while they communicate through a network. It includes technologies such as firewalls, encryption, VPNs, monitoring systems, and access controls.
Is networking important for learning cybersecurity?
Yes. Networking helps cybersecurity professionals understand how computers communicate, how attackers move between systems, and how network threats occur. Knowledge of IP addresses, ports, protocols, DNS, routing, and firewalls is especially valuable.
What is the difference between networking and network security?
Networking focuses on connecting devices and enabling communication between them. Network security focuses on protecting those connections, devices, and transmitted data against unauthorized access, malware, cyberattacks, information theft, and other security risks.
What are the main types of network security?
Common types include firewalls, intrusion detection and prevention, VPNs, network segmentation, access control, encryption, endpoint security, wireless security, vulnerability management, and continuous network monitoring for suspicious activities.
Can I learn cyber security without networking?
You can begin learning basic cybersecurity concepts without deep networking knowledge, but networking becomes increasingly important as you progress. Understanding communication protocols, IP addresses, ports, routing, and traffic analysis makes many security topics much easier to understand.