Cybersecurity work involves protecting computer systems, networks, applications, and sensitive information from digital threats. As organizations increasingly depend on technology, cybersecurity professionals help keep essential services secure and operational. Their daily responsibilities may include monitoring suspicious activity, investigating security alerts, assessing vulnerabilities, and improving protective measures that reduce the risk of cyberattacks.
Understanding what cybersecurity work looks like can help students, beginners, and career changers decide whether the field matches their interests. Cybersecurity includes a wide range of responsibilities, from technical investigations to security policy development and employee training. This guide explains a typical cybersecurity workday, common job roles, workplace environments, essential skills, career challenges, and opportunities for professional growth.
What Does Cybersecurity Work Look Like?
Cybersecurity work involves identifying, preventing, detecting, and responding to threats affecting digital systems and information. Professionals use security technologies, established procedures, and analytical skills to protect organizational resources. Their responsibilities vary according to job titles, industry requirements, company size, and the complexity of the systems they manage.
A cybersecurity analyst may spend much of the day reviewing security alerts and investigating suspicious activity. A security engineer might configure protective tools, improve network defenses, or support infrastructure projects. Meanwhile, governance and compliance specialists often focus on security policies, risk assessments, and organizational requirements.
Cybersecurity is not always about responding to active attacks. Much of the work involves prevention, maintenance, planning, documentation, and communication. Effective security teams combine technical safeguards with practical processes to reduce risks and help employees use digital systems safely.
A Typical Day in the Life of a Cybersecurity Professional
A typical cybersecurity workday may begin with reviewing alerts, emails, and reports from security monitoring systems. Professionals check whether unusual events occurred and determine which issues require attention. Depending on the organization, they may also review updates about newly discovered vulnerabilities or changes affecting important infrastructure.
During the day, cybersecurity professionals might investigate alerts, attend meetings, review access permissions, or coordinate system improvements. Some tasks involve analyzing technical information, while others require communicating with colleagues. Security teams often work with network administrators, software developers, and business departments to resolve problems.
The working day may end with documenting investigations, updating security records, and preparing information for other team members. However, schedules differ significantly between cybersecurity positions. Security operations centers may operate continuously, while governance, consulting, and project-focused roles commonly follow more predictable working arrangements.
Monitoring Networks and Detecting Security Threats
Security monitoring is a major responsibility in many cybersecurity jobs. Professionals examine information from computers, servers, networks, and applications to identify potential threats. Monitoring tools generate alerts when unusual activity occurs, but security analysts must determine whether the activity represents a genuine problem.
Organizations often use security information and event management platforms, commonly called SIEM systems. These platforms collect and organize security events from different sources. Analysts review alerts, investigate suspicious patterns, and compare technical evidence to understand whether unauthorized activity may have occurred.
Monitoring requires patience, attention to detail, and analytical thinking. Not every alert indicates an actual cyberattack, and some unusual events have harmless explanations. Professionals must carefully assess the available evidence before deciding whether further investigation or defensive action is necessary.
Investigating Cybersecurity Incidents
Incident investigation involves examining events that may affect the confidentiality, integrity, or availability of digital systems. Security professionals collect relevant information, identify potentially affected resources, and determine the nature of suspicious activity. Their findings help organizations understand what happened and decide how to respond.
An investigation might begin after an employee reports a suspicious email or a monitoring system detects unusual account activity. Analysts review appropriate logs, system information, and available security evidence. They document observations and coordinate with authorized teams to determine whether protective action is required.
Incident investigations can be complex because digital environments contain many connected systems. Professionals must avoid making assumptions before reviewing evidence. Clear documentation, structured procedures, and communication help security teams manage incidents while supporting reliable recovery and future security improvements.
Preventing Cyberattacks Before They Happen
Preventive security work focuses on reducing vulnerabilities and limiting opportunities for unauthorized access. Cybersecurity teams regularly review system configurations, software updates, account permissions, and existing protective controls. These activities help identify weaknesses before they become serious operational problems.
Common preventive measures include multifactor authentication, network segmentation, secure configuration management, and vulnerability remediation. Security professionals may also recommend stronger access controls and improvements to backup procedures. Each measure contributes to a layered approach rather than depending on a single security technology.
Prevention also involves understanding the organization’s systems and everyday working practices. Security measures must support legitimate business activities while managing risks appropriately. Professionals evaluate how protective changes could affect employees, customers, and essential services before recommending implementation.
What Does a Cybersecurity Analyst Do?
A cybersecurity analyst helps organizations identify and respond to potential security threats. Typical responsibilities include reviewing alerts, investigating suspicious activity, checking vulnerabilities, and maintaining security documentation. Analysts may work independently on routine tasks or collaborate with experienced team members during more complicated investigations.
Many analysts use monitoring dashboards, security logs, endpoint protection systems, and incident tracking platforms. Their work requires understanding normal system behavior so unusual events can be recognized. They may also prepare summaries explaining what was discovered and whether additional security improvements are necessary.
Entry-level analysts often begin with clearly defined responsibilities and receive guidance from experienced professionals. As their skills develop, they may handle more complex investigations and contribute to security improvement projects. The exact role differs between organizations, so job descriptions should be reviewed carefully.
What Does a Cybersecurity Engineer Do?
Cybersecurity engineers design, implement, and maintain technical controls that protect digital infrastructure. Their responsibilities may involve firewalls, identity systems, endpoint protection platforms, cloud environments, and network security technologies. They help organizations build secure systems that support everyday business operations.
A security engineer might evaluate existing configurations, investigate technical weaknesses, or deploy approved security improvements. They often collaborate with infrastructure specialists and software teams to ensure protective measures work correctly. Testing changes before wider deployment can help reduce disruptions and identify unexpected problems.
Engineering positions generally require strong technical knowledge and practical experience with relevant systems. Professionals need to understand how protective tools interact with networks, applications, and user environments. Good communication is also important because security improvements frequently involve multiple departments.
What Does a Security Operations Center Look Like?
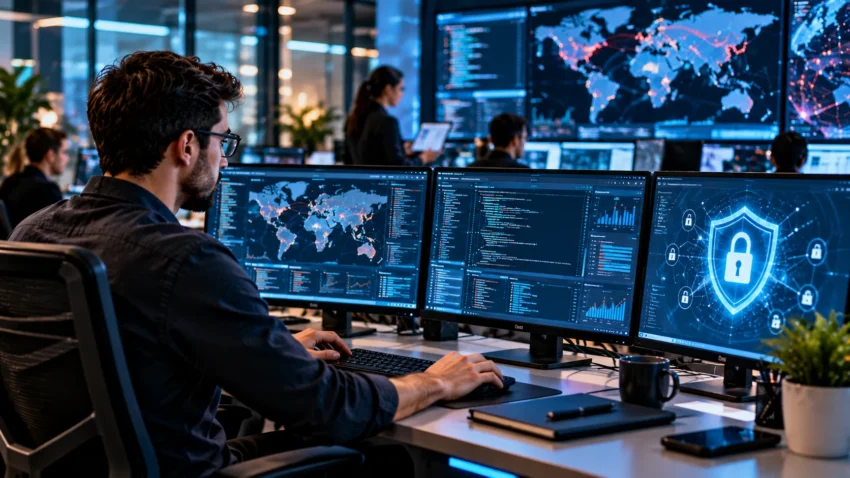
A security operations center, commonly called a SOC, is a team or facility responsible for monitoring and responding to digital security events. Some organizations operate dedicated physical centers, while others use distributed or remote teams. SOC employees work with monitoring platforms and structured procedures to manage incoming security alerts.
A typical SOC environment includes security dashboards, incident management systems, and communication tools. Analysts review suspicious events and escalate complicated cases when necessary. Different levels of analysts may handle different responsibilities, although team structures vary across organizations.
Because cyber threats can occur at any time, some SOC teams operate around the clock. Employees may work rotating shifts, including evenings or weekends. Other organizations use external monitoring providers or different staffing arrangements, making working conditions dependent on the employer and service requirements.
Cybersecurity Work in Cloud Security
Cloud security professionals protect applications, data, and computing resources hosted on cloud platforms. Their responsibilities include reviewing access permissions, checking configurations, monitoring activity, and supporting secure deployment processes. As businesses adopt cloud technologies, these tasks have become important parts of modern cybersecurity operations.
Cloud environments often contain multiple services that interact through networks and application interfaces. Security specialists help ensure that resources are configured appropriately and that access remains limited to authorized users. They may also review logging capabilities, encryption settings, and automated security checks.
Cloud security work requires understanding the division of responsibilities between service providers and customers. Professionals must recognize which protections are managed by the provider and which remain the organization’s responsibility. This knowledge helps reduce configuration errors and supports effective security management.
Cybersecurity Work in Application Security
Application security specialists focus on identifying and reducing security weaknesses in software programs and websites. They collaborate with development teams to support secure design, coding, testing, and maintenance. Their work helps organizations protect applications that process sensitive information or provide important digital services.
Daily tasks may include reviewing software requirements, examining security testing results, and discussing potential vulnerabilities with developers. Specialists may also assess third-party software components and recommend appropriate security controls. The objective is to identify risks early and support secure software development practices.
Application security work requires technical understanding alongside effective teamwork. Security recommendations must be practical and clearly communicated to development teams. Professionals who enjoy programming, problem-solving, and software architecture may find this area particularly interesting.
What Does Cybersecurity Risk Management Work Involve?
Cybersecurity risk management focuses on identifying digital risks and helping organizations make informed decisions about them. Professionals examine possible threats, existing vulnerabilities, and potential business consequences. Their work supports decisions about which security improvements should receive attention and resources.
Risk specialists may conduct assessments, review security policies, and document findings for management teams. They often work with different departments to understand how technology supports business activities. Their recommendations help organizations balance operational needs with appropriate protection.
This area generally involves more reporting, analysis, and communication than continuous technical monitoring. However, understanding basic cybersecurity concepts remains important. People who enjoy organization, research, and business decision-making may find risk management and governance roles appealing.
Common Tools Used by Cybersecurity Professionals
Cybersecurity professionals use different tools depending on their responsibilities and working environments. Common categories include SIEM platforms, endpoint detection systems, vulnerability scanners, firewalls, and identity management solutions. These technologies help teams collect information, detect suspicious behavior, and implement protective measures.
Security analysts may use dashboards to investigate events, while engineers rely on configuration and management platforms. Cloud security professionals work with cloud-native monitoring services and access controls. Governance specialists may use risk tracking and compliance management software to organize assessments and documentation.
Learning tools is important, but understanding the underlying security concepts is even more valuable. Software platforms change, while principles such as access control, secure configuration, and incident management remain widely applicable. Beginners should focus on foundational knowledge before attempting to master numerous products simultaneously.
Skills You Need to Work in Cybersecurity
Cybersecurity requires a combination of technical knowledge and professional skills. Important technical foundations include computer networking, operating systems, authentication, basic programming concepts, and information security principles. These subjects help professionals understand how digital systems function and where security weaknesses may develop.
Analytical thinking is especially valuable because cybersecurity work often involves interpreting incomplete or unfamiliar information. Professionals must distinguish relevant evidence from unrelated events and communicate findings clearly. Attention to detail, curiosity, and organized problem-solving can support effective security investigations.
Teamwork and continuous learning are equally important. Cybersecurity professionals regularly interact with colleagues who have different technical backgrounds. Explaining security concerns in straightforward language helps organizations make better decisions and encourages cooperation between security teams and other departments.
Is Coding Required for Cybersecurity Jobs?
Coding is useful in many cybersecurity roles, but advanced programming is not required for every position. Security analysts may benefit from understanding basic scripts and log formats, while application security specialists often need stronger programming knowledge. Governance and risk roles may involve relatively little direct coding.
Languages such as Python, JavaScript, and SQL can be useful depending on the specialization. Scripting skills may help automate repetitive administrative tasks or process security information. However, beginners should first develop a clear understanding of systems, networks, and basic security concepts.
Learning programming gradually can create additional career opportunities without making it the only measure of professional ability. Someone interested in policy, compliance, or security awareness may follow a different learning path from a technical engineer. The most relevant skills depend on the responsibilities of the intended position.
Is Cybersecurity Work Stressful?
Cybersecurity work can involve pressure, particularly when responding to serious incidents or urgent system problems. Some professionals must make important decisions under time constraints while coordinating with different teams. However, stress levels vary considerably according to job responsibilities, organizational resources, and working conditions.
Routine cybersecurity tasks may be more predictable than emergency incident response. Positions involving governance, documentation, or long-term security projects can have different daily demands. Even within technical roles, supportive management and clear procedures can influence how manageable workloads feel.
Anyone considering cybersecurity should understand the expectations of specific positions rather than assuming every role involves constant emergencies. Reviewing shift requirements, on-call responsibilities, and professional development opportunities can help applicants evaluate employers. Sustainable work practices and reasonable recovery time are important in this field.
Do Cybersecurity Professionals Work Remotely?
Many cybersecurity responsibilities can be performed remotely because professionals use digital tools to monitor systems, review configurations, and communicate with colleagues. Remote work may be available in security analysis, cloud security, consulting, governance, and certain engineering positions. However, availability depends on employer policies and security requirements.
Some organizations require employees to work on-site when managing sensitive infrastructure or restricted environments. Others use hybrid arrangements combining office attendance with remote responsibilities. Positions involving specialized equipment or physical security systems may require more frequent workplace access.
Remote cybersecurity work still requires secure communication, appropriate device protection, and effective collaboration. Employers may establish strict access requirements for sensitive systems. Applicants should review individual job descriptions carefully because remote opportunities and workplace expectations differ between organizations.
How Many Hours Do Cybersecurity Professionals Work?
Cybersecurity working hours vary according to the role, organization, and operational requirements. Many professionals follow conventional full-time schedules during normal business hours. However, security operations teams and incident response specialists may need alternative arrangements to provide coverage outside standard working periods.
Some cybersecurity positions involve rotating shifts, weekend responsibilities, or on-call availability. Others focus on project-based tasks and maintain more predictable schedules. Understanding these differences is important because the cybersecurity industry includes many specializations with distinct working conditions.
Work schedules should be considered alongside salary, learning opportunities, and professional responsibilities. People who prefer stable daytime hours may explore positions with predictable operational requirements. Reviewing employment contracts and discussing expectations during interviews can help clarify the actual demands of a particular cybersecurity job.
How to Start Working in Cybersecurity
Starting a cybersecurity career usually begins with learning basic computer and networking concepts. Understanding operating systems, internet communication, user accounts, and common threats provides a practical foundation. These subjects make it easier to understand more advanced security topics and specialized technologies.
Beginners can develop skills through structured courses, beginner-friendly certifications, and authorized practical training environments. Educational labs and simulated exercises allow learners to explore security concepts without interfering with real systems. Creating documentation about completed projects can also demonstrate understanding and communication abilities.
Entry-level opportunities may include junior security analyst positions, security support roles, or related IT jobs that develop relevant experience. Requirements differ between employers, and some cybersecurity positions expect previous technical experience. Building foundational knowledge and applying for suitable opportunities can support long-term career development.
Career Growth and Opportunities in Cybersecurity
Cybersecurity offers several possible career paths, including security analysis, engineering, cloud protection, incident response, digital forensics, and governance. Professionals may begin with general responsibilities before developing expertise in a particular area. Specialization allows individuals to focus on tasks that match their technical interests and preferred working styles.
Career development often involves expanding practical knowledge, completing relevant training, and gaining experience with different technologies. Some professionals move into senior technical positions, while others pursue management or consulting responsibilities. The most suitable path depends on individual skills, career goals, and available opportunities.
The cybersecurity field changes as organizations adopt new technologies and face evolving digital risks. Professionals benefit from keeping their knowledge current and developing adaptable problem-solving skills. A willingness to learn can help individuals navigate different roles and contribute effectively throughout their careers.
Conclusion
Cybersecurity work involves much more than stopping hackers or monitoring computer screens. Professionals protect networks, applications, cloud environments, devices, and information through a combination of technical safeguards and organizational processes. Their daily responsibilities may include investigating alerts, managing risks, improving security controls, and supporting incident response activities.
The experience of working in cybersecurity depends heavily on the chosen specialization. Security analysts focus on detection and investigation, engineers develop protective infrastructure, and governance specialists evaluate risks and policies. Working hours, remote opportunities, technical requirements, and daily challenges also vary between employers and positions.
For beginners interested in cybersecurity careers, understanding the different job responsibilities is an important first step. Developing networking knowledge, security fundamentals, analytical thinking, and communication skills can provide a strong foundation. With practical learning and thoughtful career planning, cybersecurity can offer diverse opportunities to contribute to safer digital systems.
Frequently Asked Questions (FAQs)
What does a cybersecurity professional do every day?
Cybersecurity professionals may monitor alerts, investigate suspicious activity, review vulnerabilities, manage security controls, and document findings. Daily responsibilities depend on the job title, organization, and technical environment.
Is cybersecurity a difficult job?
Cybersecurity can be challenging because it requires problem-solving and continuous learning. However, difficulty varies across roles, and beginners can develop the necessary knowledge gradually through training and practical experience.
Do cybersecurity jobs require coding?
Not all cybersecurity jobs require advanced coding skills. Programming and scripting are useful in technical specializations, while governance, compliance, and certain analyst roles may place greater emphasis on other skills.
Can cybersecurity professionals work from home?
Yes, some cybersecurity positions offer remote or hybrid work arrangements. Availability depends on employer policies, job responsibilities, security restrictions, and whether the position requires physical access to equipment.
Is cybersecurity a good career for beginners?
Cybersecurity provides several potential career paths for people interested in technology and digital protection. Beginners can start with networking, operating systems, fundamental security concepts, and authorized practical training.